2 minutes
CVE-2025-22139: Cross-Site Scripting (XSS) Reflected endpoint configuracao_geral.php parameter msg
⚠ Replicated advisory. This post reproduces an advisory originally researched and published under the CVE Hunters. It is republished here for reference. The original disclosure followed coordinated vulnerability disclosure and the rules of the CVE Program.
🔗 Original advisory: https://www.cvehunters.com/p/cve-2025-22139/
📋 CVE record: CVE-2025-22139
CVE Publication: https://www.cve.org/CVERecord?id=CVE-2025-22139
Summary
A Reflected Cross-Site Scripting (XSS) vulnerability was identified in the configuracao_geral.php endpoint of the WeGIA application. This vulnerability allows attackers to inject malicious scripts in the msg_c parameter.
Details
Vulnerable Endpoint: html/configuracao/configuracao_geral.php
Parameter: msg
The application fails to validate and sanitize user inputs in the msg_c parameter. This lack of validation permits the injection of malicious payloads, which are reflected back to the user's browser in the server's response and executed within the context of the victim's browser.
POC
Payload:
"><script>alert(document.cookie)</script>
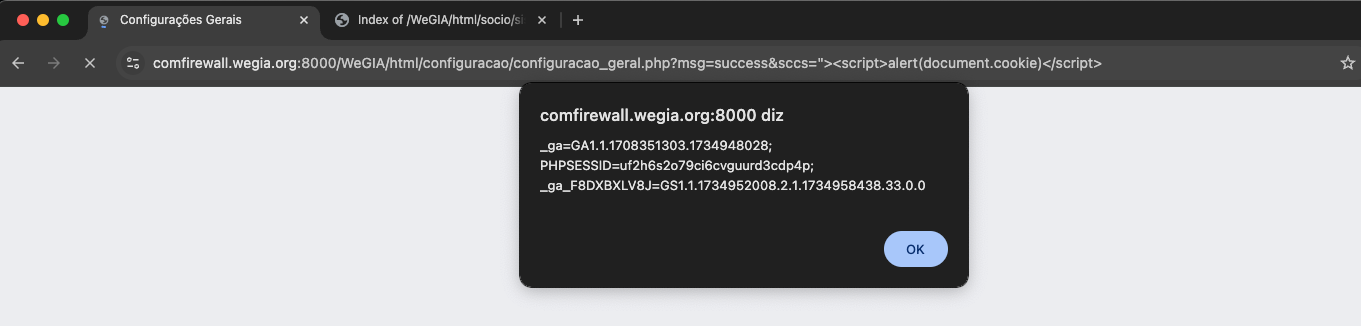
Impact
This vulnerability allows an attacker to:
- User actions: Attackers can perform any action the user can, such as viewing, modifying, or initiating interactions with other users.
- Data theft: Attackers can exfiltrate data or install malware on the user's machine.
- Account compromise: Attackers can manipulate or steal cookies, or compromise confidential information.
- Malicious code: Attackers can execute malicious code on the user's system.
- Business reputation damage: Attackers can deface a corporate website or spread misinformation.
- Misdirection: Attackers can change the instructions given to users, which can be dangerous if the target is a government website or provides vital resources.
Reference
https://github.com/LabRedesCefetRJ/WeGIA/security/advisories/GHSA-xrjq-57mq-4hf8
Finder

Contributors


By: CVE-Hunters